

Browser Sandboxing Explained
A browser sandbox is a security boundary that limits what web content can do on a computer. Modern websites run active code for video, games, advertising, messaging, and many ordinary page features. That code needs access to browser services, but it should not be able to roam through personal files, start arbitrary programs, or control hardware. A sandbox places the process handling a page in a restricted environment. The page can use the carefully defined capabilities the browser exposes, while direct access to sensitive operating-system resources is blocked or tightly mediated. The restriction follows the process even when a page’s code behaves unexpectedly.
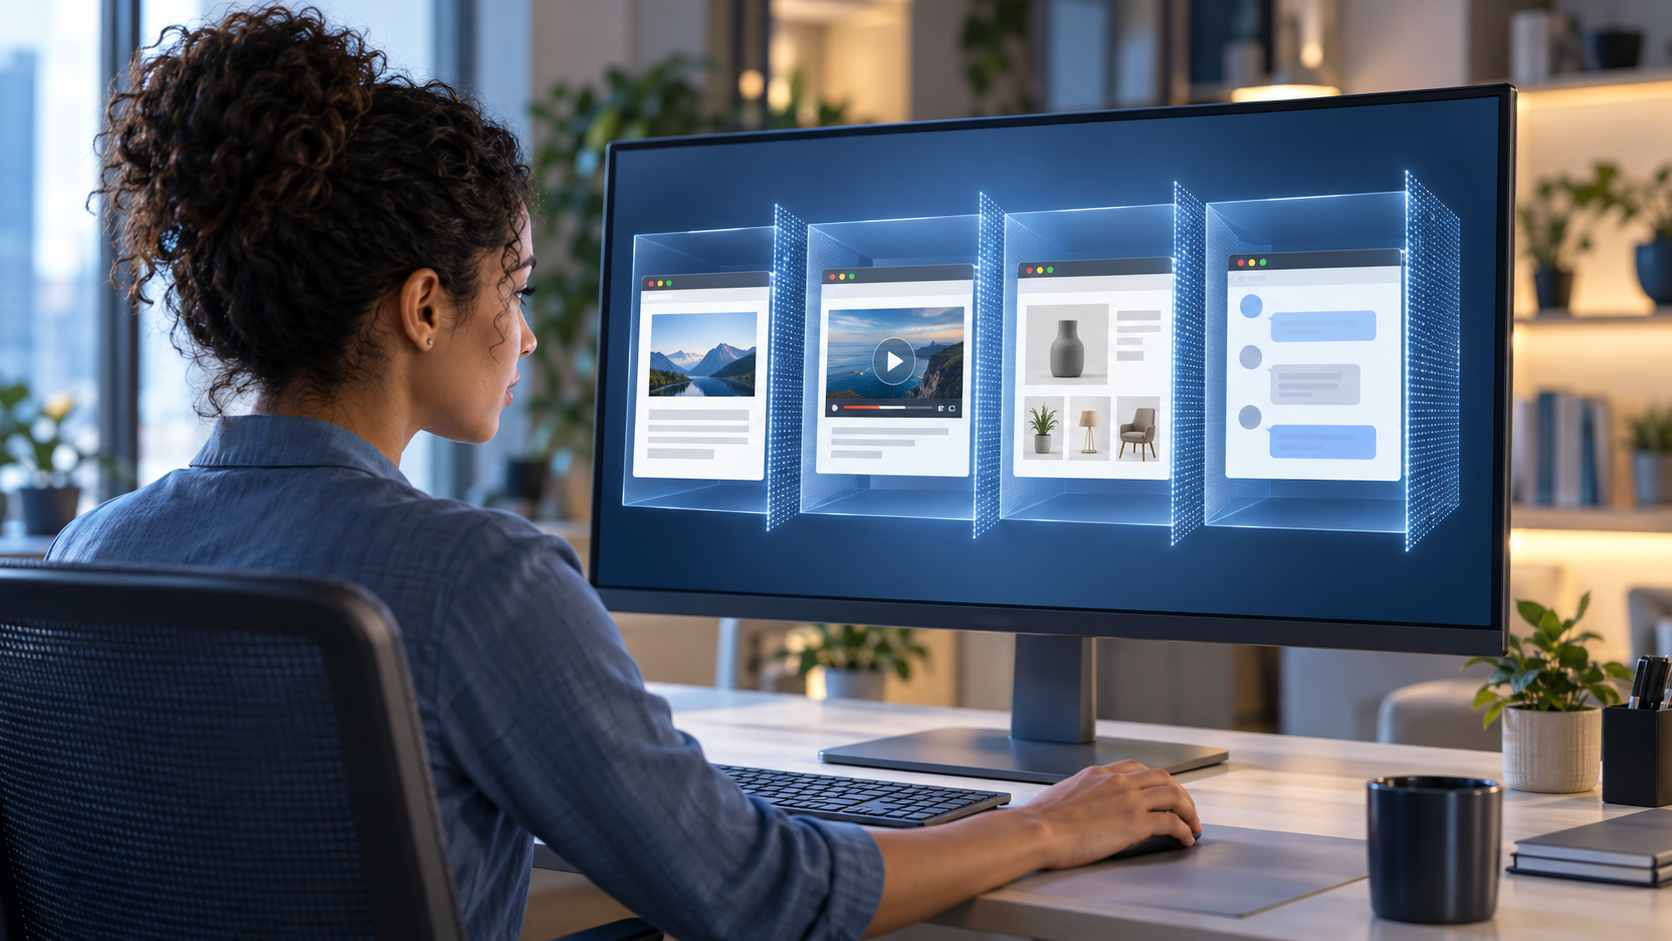
Most major browsers use a multi-process design. A relatively privileged browser process manages windows, tabs, downloads, permissions, and other trusted work. Separate renderer processes interpret HTML, CSS, and JavaScript and turn them into the pages people see. Renderers face a large amount of untrusted input, so browsers run them with fewer rights. If a renderer asks to read a file, use a device, or perform another protected action, the request must pass through a broker or browser process that checks whether the operation is allowed. This design also lets a browser terminate or restart a failed renderer without closing every tab.
That separation changes what happens when attackers exploit a flaw. Without a sandbox, a bug in page rendering might immediately give malicious code the same access as the signed-in user. Inside a sandbox, the attacker may gain control of a renderer yet remain unable to reach most of the system. This containment does not erase the bug, but it can prevent one failure from becoming a full computer compromise. An attacker often needs a second vulnerability, sometimes called a sandbox escape, to cross the boundary and obtain broader privileges. Requiring that additional step raises the cost and complexity of a successful attack.
Site isolation adds another layer. Where the sandbox separates renderers from the operating system, site isolation tries to keep content from different sites in different renderer processes. That helps reduce the chance that a compromised page can inspect another site’s secrets, such as account information loaded in a neighboring tab. The exact process model varies by browser and available memory, but the principle is consistent: do not place every website and every trust level into one shared execution space. The tradeoff is higher memory use because more separate processes may remain active.
Sandboxes also work with other controls. Browsers validate messages between processes, restrict dangerous system calls, require permission for cameras and microphones, and update frequently when vulnerabilities are discovered. Operating systems provide mechanisms such as low-integrity processes, namespaces, access tokens, and system-call filters that browsers combine in different ways. These defenses are strongest when the browser and operating system are current, because a sandbox depends on both application design and the platform enforcing its restrictions correctly. Browser vendors test these boundaries and harden the interfaces that connect restricted and privileged components.
A sandbox is therefore damage control, not a promise that browsing is risk-free. Phishing pages can still trick people into revealing information, malicious extensions may receive powerful permissions, and a chain of software flaws can sometimes escape containment. Users should install updates, review extension access, and treat unexpected downloads and permission prompts cautiously. The important idea is that a web page should begin with minimal authority. When a flaw occurs, the browser tries to keep the failure confined to the smallest possible compartment. That least-privilege approach turns a single barrier into part of a layered defense. Similar compartmentalization is used for graphics work and other components whose inputs or privileges differ. The exact boundaries evolve as browsers add features and respond to newly discovered attacks.
A restricted renderer handles untrusted page code while privileged browser services remain outside the boundary.
Protected operations go through controlled inter-process messages, where the browser can validate and approve them.
It cannot prevent phishing, unsafe extensions, or every multi-step exploit, so updates and careful permissions still matter.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.