

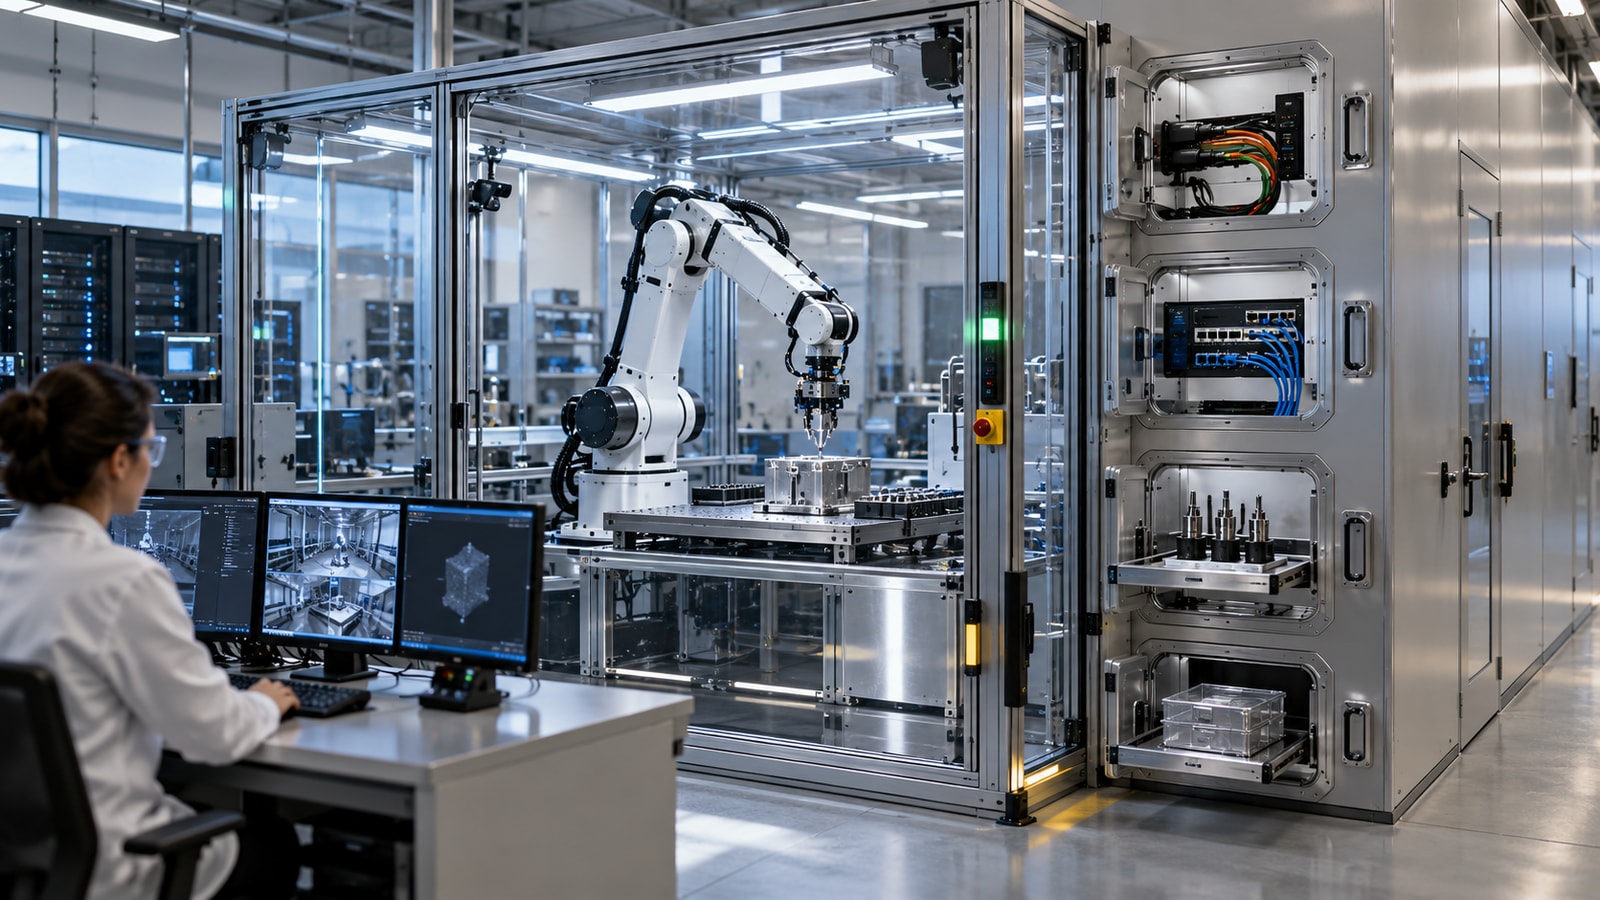
AI Sandboxing Explainer
AI sandboxing places an AI model, agent, or related workload inside an isolated environment. The sandbox restricts what the process can read, write, execute, contact, and consume if it behaves unexpectedly or handles malicious content.
Controls can include temporary containers or virtual machines, blocked host paths, limited tool allowlists, scoped credentials, restricted network access, and CPU, memory, time, or spending limits. Sensitive production systems remain outside the boundary.
Sandboxing reduces the blast radius but does not make untrusted behavior safe by itself. Weak isolation, shared devices, broad credentials, open network routes, or persistent storage can create escape paths and cross-tenant exposure.
Teams test the boundary, monitor unusual access, clear temporary artifacts, and rebuild environments from known images. The sandbox should match the workload’s risk, with stronger separation for third-party models, autonomous tools, and sensitive data.
AI sandboxing runs models, agents, or untrusted AI workloads inside isolated environments with restricted files, credentials, tools, networks, and resources.
Key terms include sandbox, isolation, blast radius, container, virtual machine, allowlist, scoped credential, egress control and resource limit.
Files, tools, credentials, networks, and devices are exposed only when necessary.
A compromised or mistaken workload therefore has fewer paths to cause damage.
Configuration mistakes can quietly reconnect the sandbox to sensitive systems.
Teardown, monitoring, and boundary tests are part of the security control.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.