

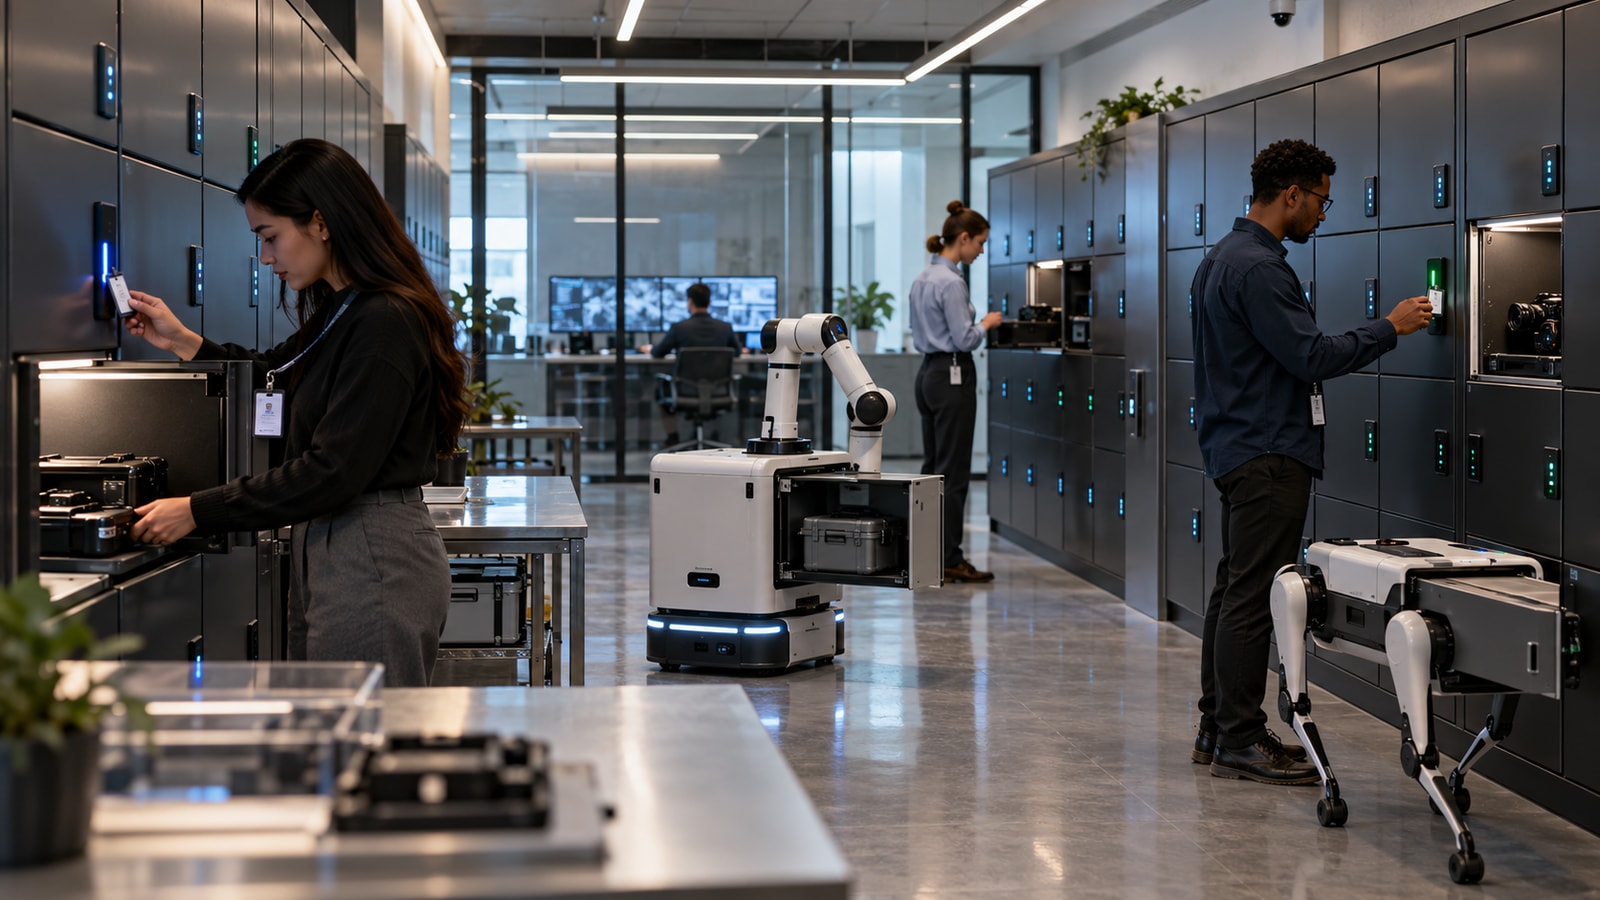
Access Control for AI Systems Explainer
Access control for AI systems determines who or what may use specific models, data, tools, environments, and administrative functions. Authentication establishes identity, while authorization decides which actions that identity is allowed to perform.
AI agents make the boundary especially important because generated tool calls can affect files, databases, messages, purchases, or infrastructure. Permissions should be checked by the execution layer, not inferred from the model’s wording or confidence.
Least privilege grants only the access required for the current task. Scoped, temporary credentials reduce harm if a prompt, plugin, account, or workload is compromised. High-impact actions may require human approval or separation of duties.
Teams review roles, log security decisions, revoke stale access, and test denied paths. Model instructions are not a security boundary, so access control should remain enforceable even when the model is confused, manipulated, or unavailable.
Access control for AI systems determines which users, services, models, agents, and tools may reach particular data, actions, environments, and administrative functions.
Key terms include access control, authentication, authorization, least privilege, role, scope, credential, approval and separation of duties.
A model may propose an action, but a separate control verifies identity and authority.
This prevents persuasive text from granting itself access to protected resources.
Task-specific credentials limit which systems and operations are reachable.
Expiration and revocation reduce the lifetime of accidental or stolen access.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.