

Segregation of Duties Explainer
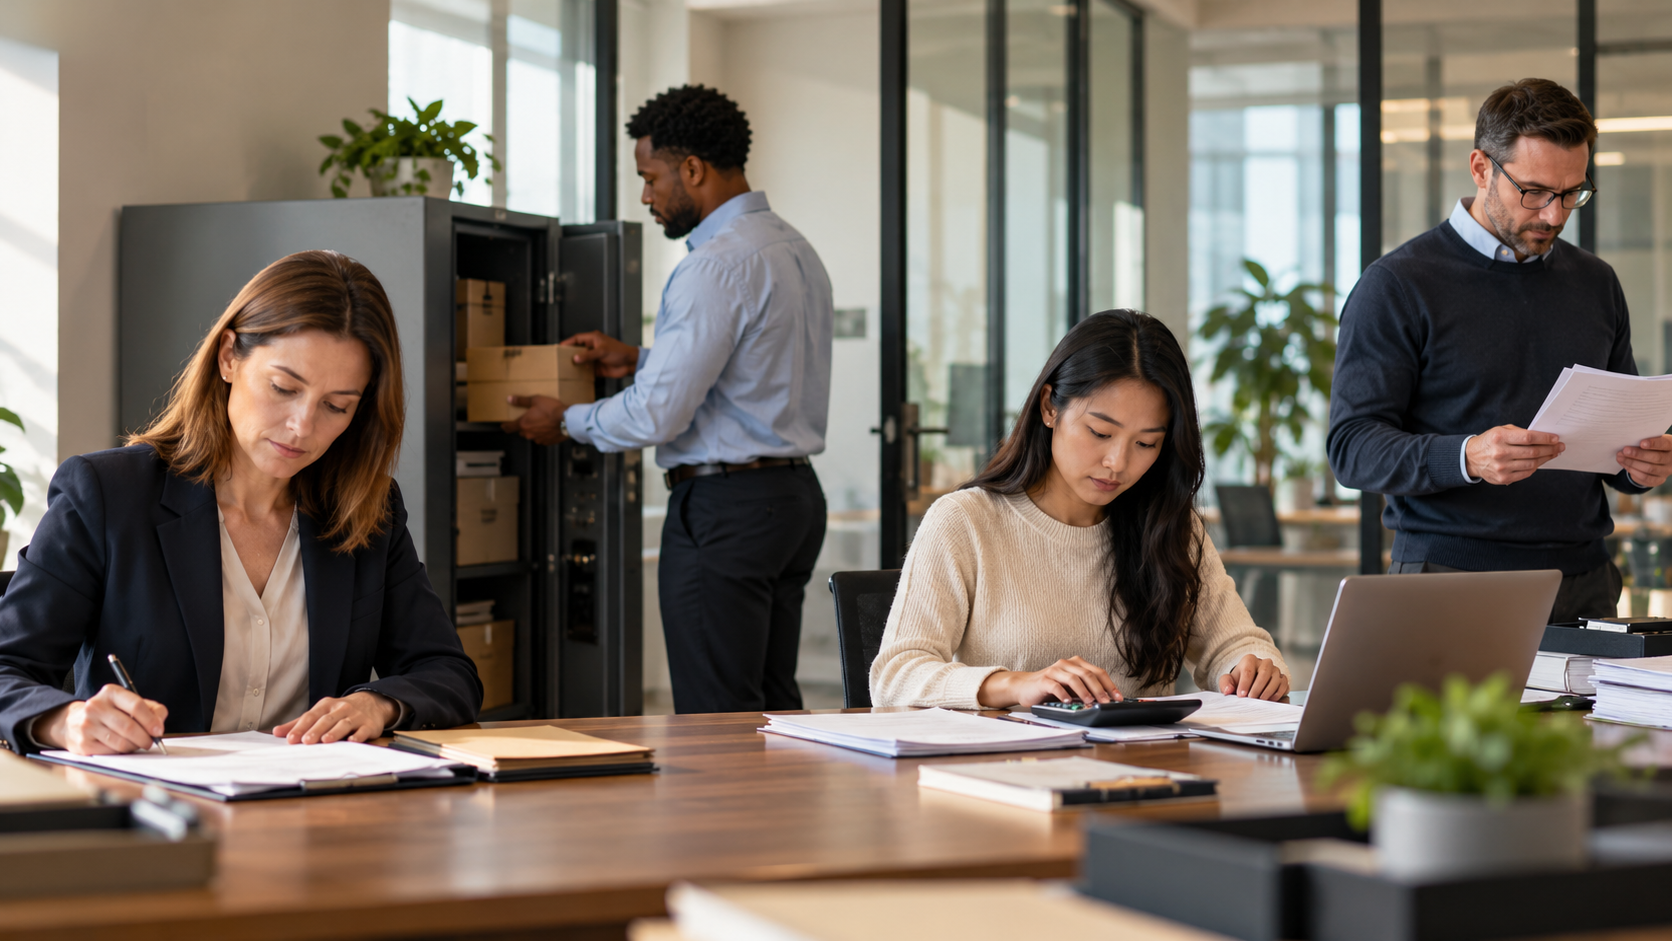
Segregation of duties is an internal-control principle that divides incompatible responsibilities among different people. A well-designed process separates authorization, custody of assets, transaction processing or recording, and independent review so one person cannot both create and conceal an improper action.
In purchasing, one person may request goods, another approve the order, receiving staff confirm delivery, and accounts payable match records before payment. In information technology, developers should not freely move their own changes into production without approval and testing.
Small organizations may lack enough staff for complete separation. Compensating controls can include owner review, bank alerts, dual approval, read-only reporting, external reconciliation, rotating duties, and restricted system permissions. The control should address the exact conflict rather than add ceremonial signoffs.
Segregation reduces risk but cannot eliminate collusion or management override. Access rights, emergency privileges, vacations, role changes, and automated workflows require periodic review. Good design assigns accountability clearly while avoiding so many handoffs that legitimate work becomes slow or opaque.
Authorization, custody, recording, and review should not sit with one person.
The split makes errors and abuse harder to conceal.
Small teams can add independent review, alerts, or dual approval.
The alternative must address the same underlying risk.
System permissions can recreate conflicts even when job titles look separate.
Review changes, exceptions, and emergency access regularly.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.