

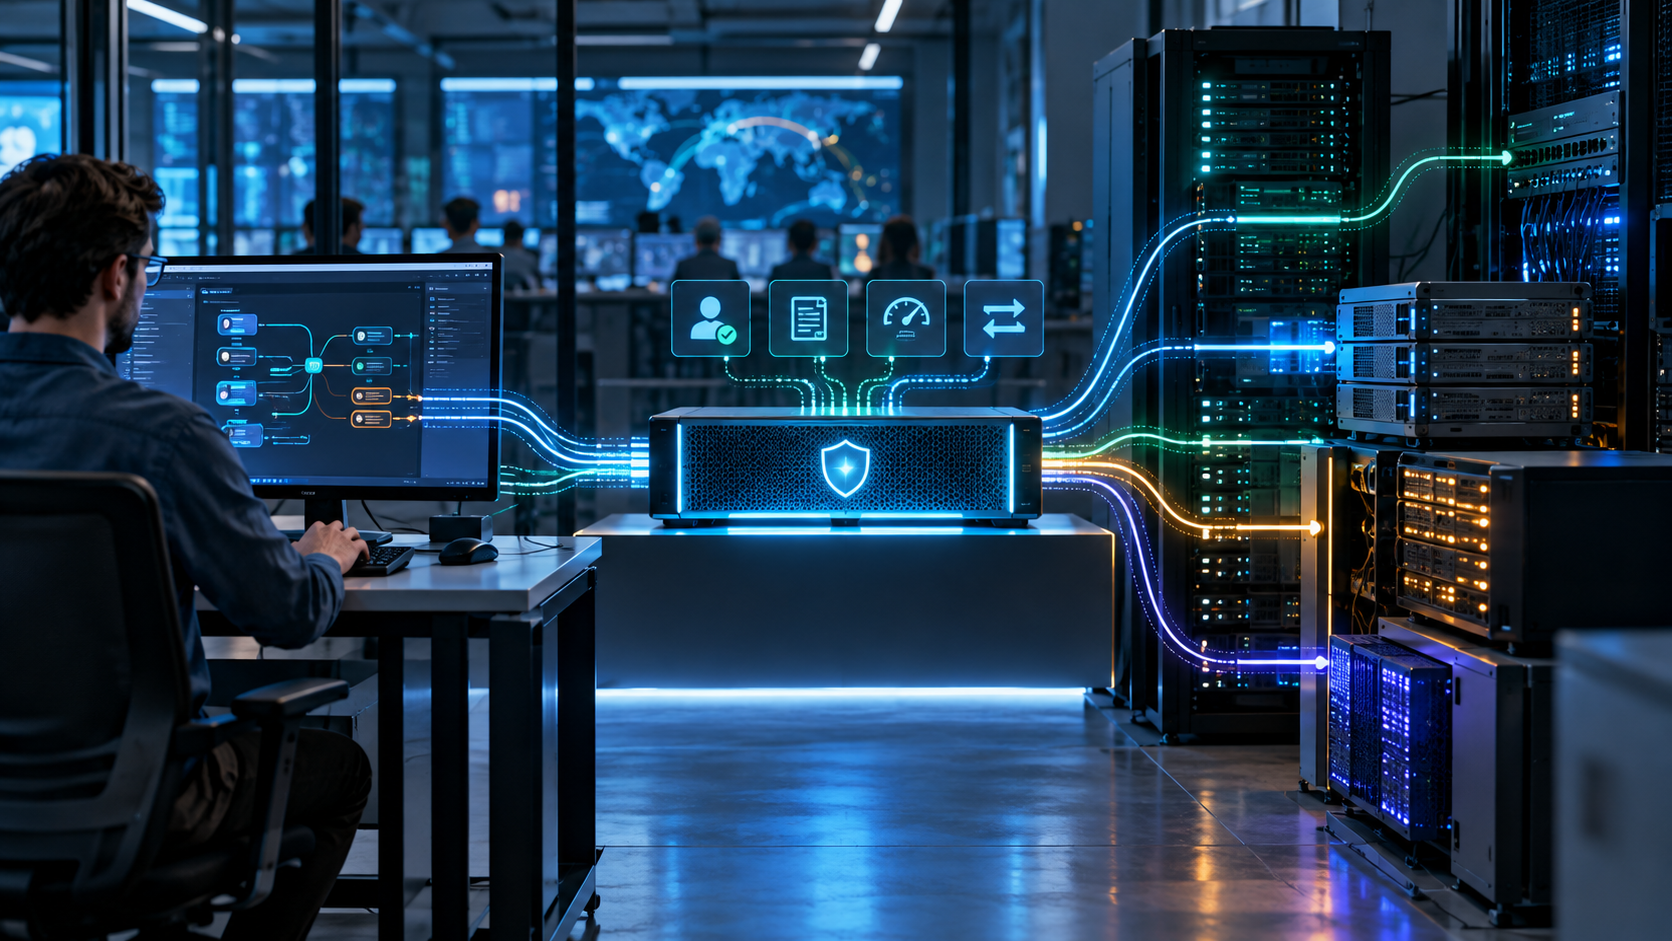
An API gateway is a controlled entry point between clients and a collection of backend application services. A mobile app, browser, partner system, or connected device sends requests to the gateway instead of addressing every internal service directly. The gateway acts as a reverse proxy: it receives a request on behalf of the back end, applies configured policies, selects the appropriate destination, and returns the resulting response. That single public surface can hide internal topology while giving clients a stable address as services move or change. The boundary also gives external developers one documented surface rather than exposing a changing list of internal hosts and ports.
Routing is the gateway’s core job. Rules can examine the hostname, URL path, HTTP method, version, header, or other request properties and forward the request to the service responsible for it. An account route might reach an identity service, while an order route reaches commerce components. The gateway may rewrite paths or headers so a public interface remains consistent with a different internal design. This allows teams to split, combine, or replace services without forcing every client to immediately learn the new layout. Versioned routes can keep older clients working during a migration while newer clients adopt a revised service contract at their own pace.
Gateways also centralize concerns that otherwise must be repeated across many services. They can terminate TLS, validate credentials or tokens, enforce quotas, limit request rates, reject oversized inputs, record access logs, and attach trace identifiers. Some cache suitable responses or filter requests against basic threats. Central policy reduces duplication, but it does not remove each service’s responsibility to authorize sensitive actions and validate data. Internal services should not assume that every request is trustworthy merely because it passed through the gateway. Logging at this layer is valuable because it connects a client-facing request with the internal calls made to satisfy it, supporting debugging and incident response.
Another pattern is aggregation. A page may need information from several microservices, and a gateway can call those services and combine their answers into one client response. That can reduce round trips over slow mobile networks. A gateway may also translate between protocols, such as exposing a conventional HTTP interface while communicating with an internal messaging or remote-procedure system. These features are useful at the edge, but too much business logic in the gateway creates tight coupling and makes deployments, testing, and failures harder to understand. Aggregation should use clear timeouts and partial-failure rules, since one slow dependency can otherwise delay an entire combined response.
An API gateway overlaps with a load balancer but is not identical to one. A load balancer primarily distributes traffic among interchangeable targets to improve capacity and availability. An API gateway is usually more aware of the API contract and applies routing, identity, transformation, quota, and observability policies across different services. One product can perform both roles, and a typical architecture may place a load balancer in front of redundant gateway instances or let the gateway balance requests among multiple instances of a chosen service. The architectural distinction is about responsibility rather than a mandatory product boundary, so diagrams should show what policies a component actually performs.
The gateway itself adds a network hop and can become a bottleneck or a single point of failure if it is poorly designed. Production deployments therefore run redundant instances, monitor latency and error rates, limit resource use, and plan how policies and routes are versioned. Teams must also protect administrative access because a bad gateway rule can affect many services at once. Used with restraint, an API gateway gives clients a simpler boundary and operators one place to enforce cross-cutting rules, while the backend remains free to evolve behind it. A well-run gateway is therefore treated as critical infrastructure, with redundancy, tested configuration changes, capacity planning, and a documented bypass or recovery plan.
A load balancer mainly distributes traffic among equivalent targets. A gateway is API-aware and can route among different services while applying identity, quota, transformation, and logging policies.
No. The gateway can enforce shared controls, but each service must still authorize sensitive actions, validate inputs, and protect its own data.
Rate limiting caps how many requests a client or credential may make during a period, helping protect capacity and enforce fair or contracted usage.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.