

A/B System Updates Explainer
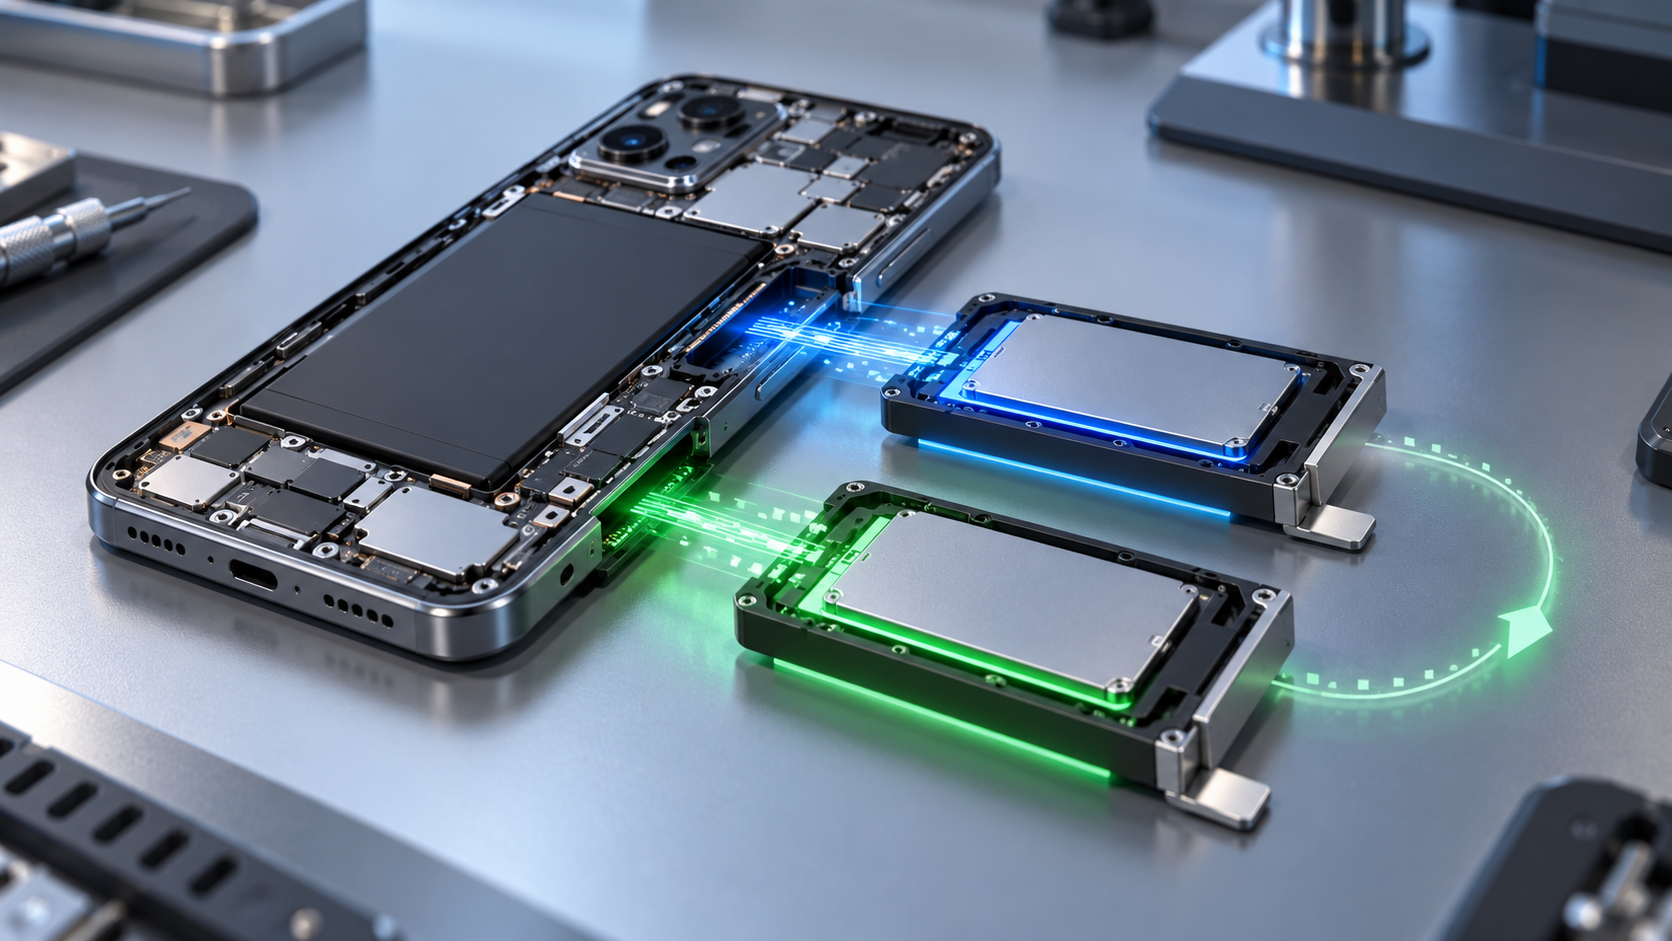
A/B system updates reduce downtime and provide a practical rollback path by keeping two sets of bootable system partitions or equivalent system states. The device runs from one slot while an updater writes the new version to the inactive slot. Because the active system is not being overwritten in place, the user can continue working during much of the installation. After the new slot is complete, the device changes its next-boot selection and restarts into the candidate version.
The slots contain the components needed to boot a compatible system, such as a kernel, low-level boot files, and system software. User data is normally stored separately so switching slots does not revert photos, messages, or application data. The updater verifies package signatures, checks device compatibility, writes each target partition, and validates the result. It then marks the new slot as bootable but not yet proven successful. Metadata records priorities, retry counts, and the current status so firmware or the bootloader can make a safe choice.
On the first candidate boot, the new system must reach a defined success point. It initializes hardware, mounts required storage, starts essential services, and marks its slot successful only after the platform considers it healthy. If the device repeatedly resets or cannot complete startup, the boot logic decreases the remaining attempts. When they are exhausted, it selects the previously working slot. This automatic fallback protects against many broken kernels, damaged system images, and power losses during the transition.
Rollback has boundaries. The old system must still understand shared user data and any firmware or security changes that happened during the update. A one-way database migration or anti-rollback security counter can make an older slot unsafe or intentionally unbootable. Update designers therefore coordinate partition formats, data migrations, bootloader behavior, and version policy. Some changes are deferred until success is confirmed, while others require forward-compatible data or a separate recovery mechanism.
Traditional A/B layouts use more storage because two complete system sets are reserved. Virtual A/B designs can use snapshots and copy-on-write storage to create a new system state without permanently duplicating every unchanged block. During installation, changed blocks go into snapshot storage; after a successful boot, a merge incorporates them into the base. The device must protect that merge from interruption and retain enough free space. The conceptual contract remains the same even when the physical layout changes: prepare a candidate without destroying the known-good state.
A/B updating is not a substitute for application backups or comprehensive testing. A new system can boot successfully yet contain a subtle functional or security regression, and user data corruption may affect both slots. Update services need signed metadata, staged rollout, telemetry, battery and storage checks, and a recovery route for devices that cannot boot either slot. Users may notice only one restart, but the safety comes from careful state management underneath. A/B updates turn installation into a controlled boot decision: build and verify an inactive candidate, try it with a limited number of attempts, declare success only after health checks, and retain the earlier slot long enough to recover when the candidate cannot start reliably.
Fleet rollout policy adds another safety layer. Operators first update a small group, compare crash and boot-success signals, and expand only when results remain healthy. A server-side pause prevents more devices from downloading a bad release, while on-device retry rules handle temporary network or power failures. Payloads may be full images or deltas from a known version; a delta saves bandwidth but requires precise verification of the starting content. Every path ends with cryptographic validation of the finished target, because an efficient transfer is useful only if the inactive slot exactly matches the authorized release.
A/B updates write a new system to an inactive slot, boot it as a candidate, and retain the prior slot for fallback. Key terms include active slot, inactive slot, bootable, successful, retry count, rollback, user data, snapshot, copy-on-write, and merge.
If the candidate slot cannot reach its success checkpoint within the allowed boot attempts, boot metadata directs the device back to the previously successful slot. Exact health criteria depend on the platform.
Shared data formats, firmware, boot components, or security counters may change in ways an older system cannot use. Designers must make migrations compatible or deliberately block rollback when returning would create corruption or a security risk.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.