What Are Adversarial Examples?
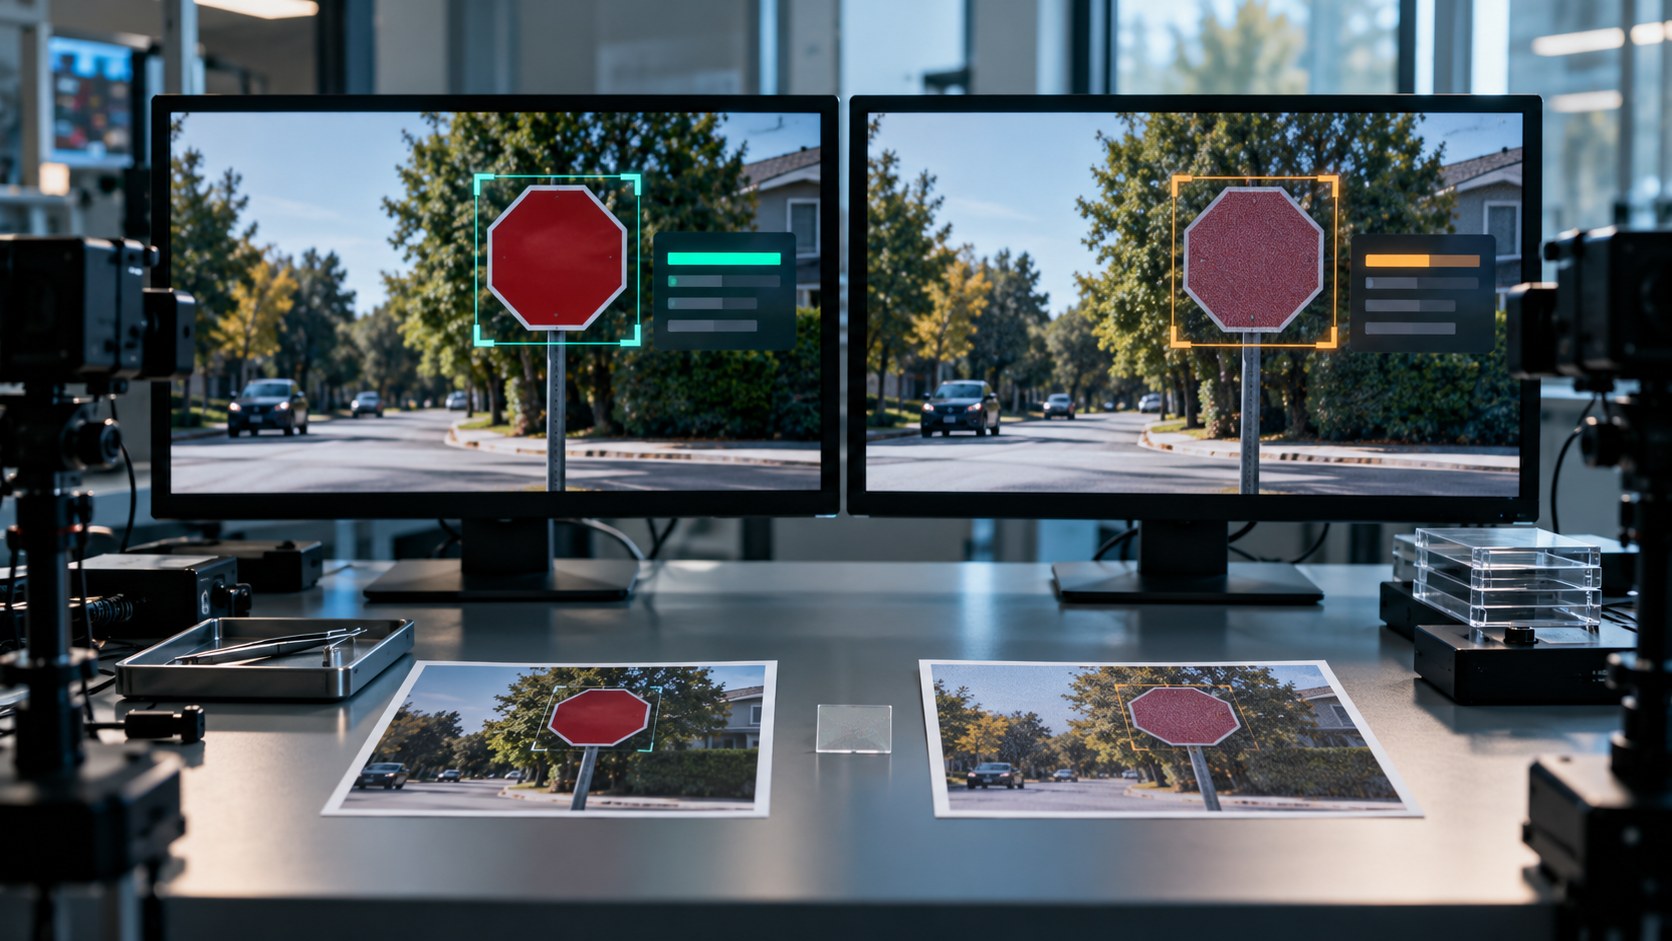
Adversarial examples are inputs deliberately altered to cause a machine-learning model to make a wrong prediction while the change may appear small or harmless.

Don't Just Read it – Explore It
Adversarial examples are inputs deliberately altered to cause a machine-learning model to make a wrong prediction while the change may appear small or harmless.
Differential privacy is a mathematical framework that limits how much the inclusion of one person’s data can change an analysis or trained model.
Model calibration measures whether predicted probabilities match how often outcomes actually occur, such as whether 70-percent predictions are right about 70 percent of the time.
AI red teaming is structured adversarial testing that probes a model or system for harmful behavior, security weaknesses, misuse paths, and failed safeguards.
Active learning lets a model choose which unlabeled examples should be sent to a human or oracle for labels so annotation effort is used strategically.
A knowledge graph represents entities and their relationships as connected nodes and labeled edges that software can query and combine.
Zero-shot learning applies prior representations or semantic descriptions to a task or class without labeled examples from that exact target.
Self-supervised learning creates training targets from the data itself so a model can learn useful representations without manual labels for every example.
Few-shot learning aims to perform a new task or recognize a new class from only a small number of labeled examples.
Regression is a machine-learning task that predicts a continuous numerical value such as demand, duration, temperature, or price.
Transfer learning reuses representations learned for one task or dataset as a starting point for a related new task.
Anomaly detection identifies observations that differ substantially from an expected pattern so they can be investigated, filtered, or handled differently.