What Is Split Learning?
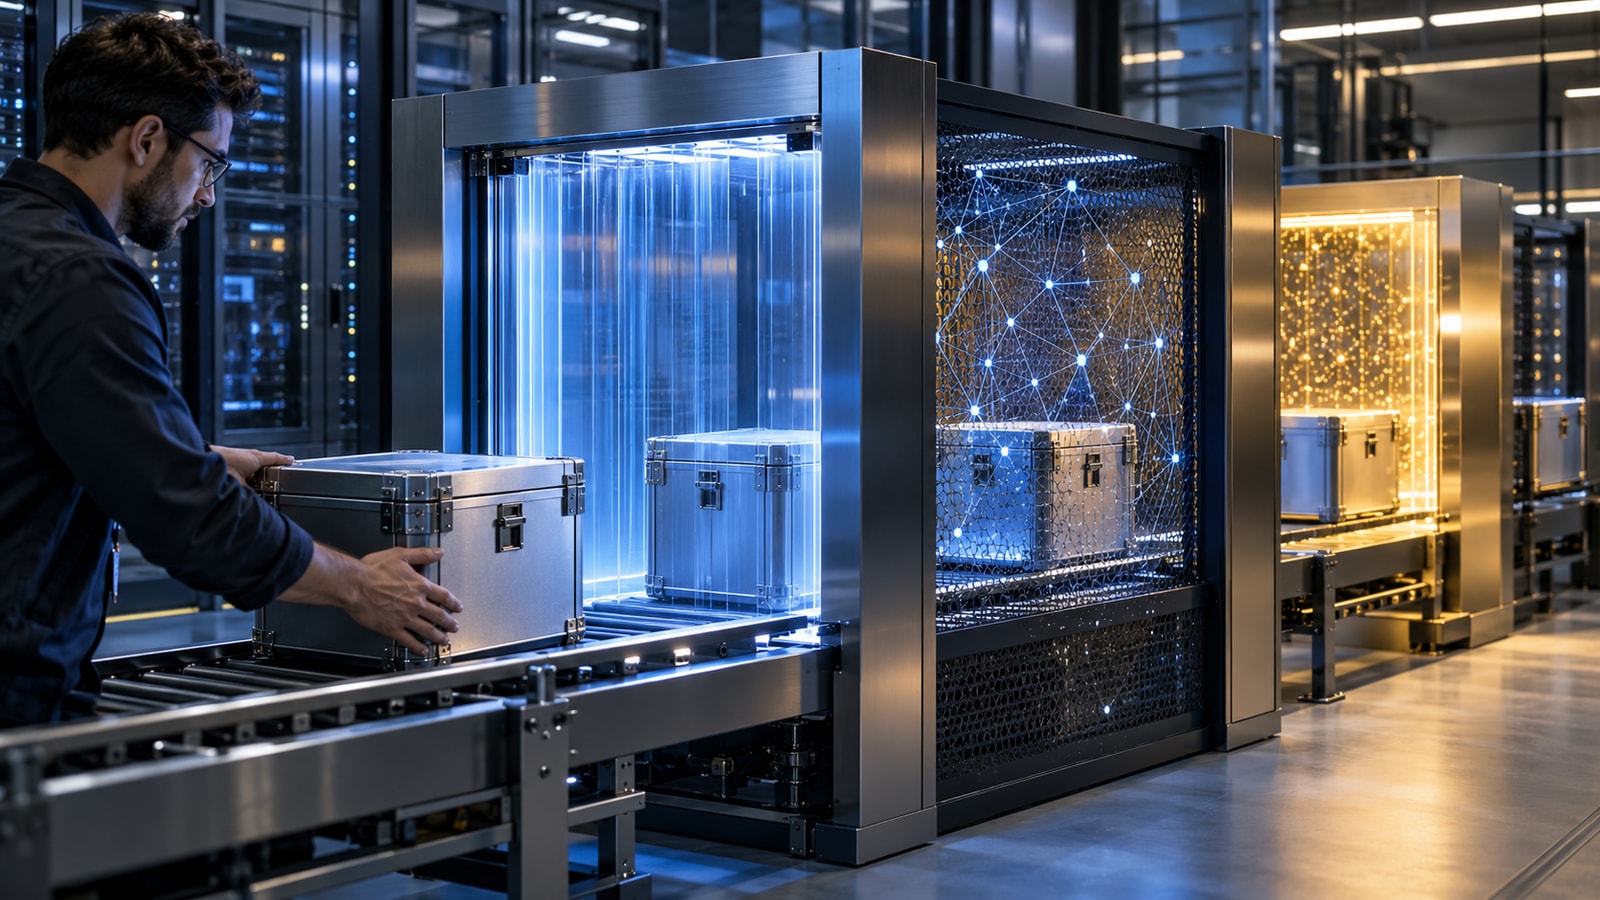
Split learning divides a neural network between participants so raw data stays with the client while intermediate activations cross the boundary.

Don't Just Read it – Explore It
Split learning divides a neural network between participants so raw data stays with the client while intermediate activations cross the boundary.
Vertical federated learning trains across organizations that hold different features about overlapping entities without pooling all raw records in one place.
Secure multi-party computation lets several participants jointly calculate an AI result while keeping their separate inputs hidden from one another.
Homomorphic encryption allows certain AI computations to run on encrypted data so the computing service does not need to see the underlying values.
Machine unlearning aims to remove the influence of selected training data from a model without always retraining the entire system from the beginning.
Privacy-preserving machine learning uses technical and organizational controls to reduce exposure of sensitive data during training, evaluation, and inference.
Randomized smoothing builds a more robust classifier by averaging a base model’s predictions across many noisy versions of the same input.
Adversarial training teaches a model with deliberately challenging inputs so it becomes less vulnerable to similar perturbations at deployment.
Certified robustness provides a mathematical guarantee that a model’s prediction will remain unchanged within a defined set of input perturbations.
A model inversion attack uses access to an AI model to reconstruct features or representative information associated with its training data.
Model extraction uses repeated access to an AI service to build a substitute that imitates its outputs or reveals aspects of the original model.
A membership inference attack tries to determine whether a specific person’s or record’s data was included in an AI model’s training set.