

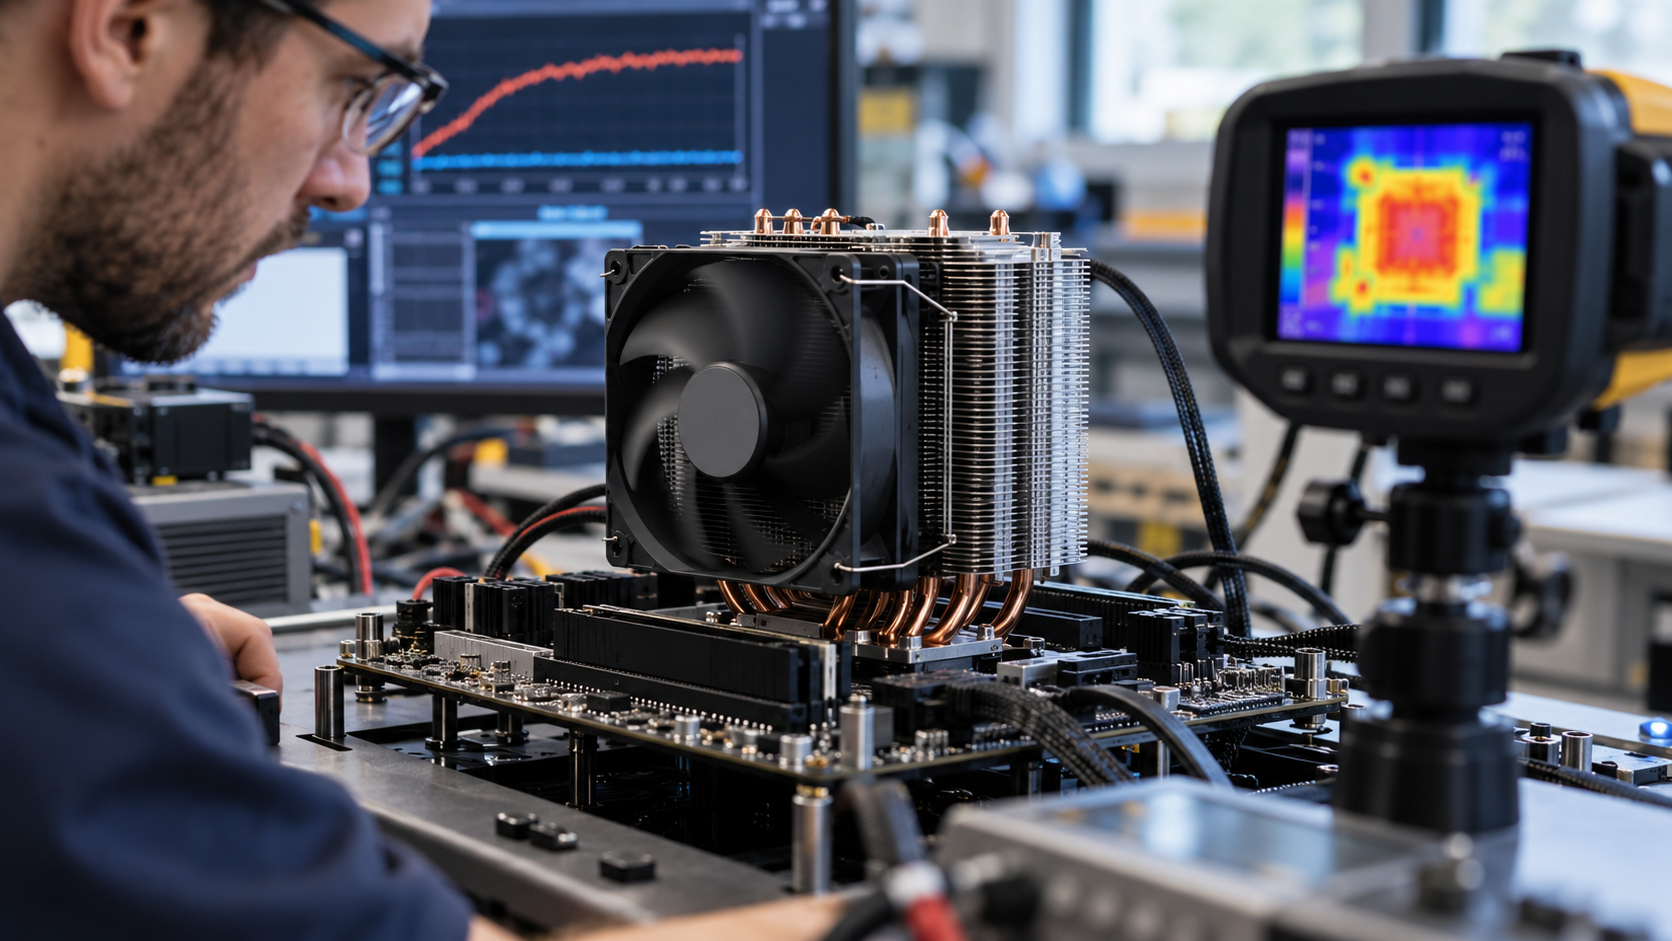
Thermal throttling lowers a chip’s operating frequency, voltage, or workload when sensors indicate that temperature, power, or current is approaching a protected limit. The useful starting point is to separate the job the technology performs from the products that implement it. Vendors may expose different controls, but compatible systems share core rules so independently built components can work together. Understanding that boundary also prevents the feature from being credited with protections it was never designed to provide. It is also useful to identify the trust boundary: which component makes a decision, which evidence it relies on, and what another component is allowed to assume afterward in normal operation.
On-die sensors and power-control logic continuously estimate operating conditions. Dynamic voltage and frequency controls reduce performance states, while fans and system firmware adjust cooling to keep components within specifications. Those parts operate under rules that define message or data formats and the conditions under which a result is accepted. Implementations also keep state because a later step often depends on what happened earlier. Logs, counters, traces, and diagnostic tools make that state observable and help distinguish a normal delay from overload, configuration error, or active attack. Performance comes from dividing work carefully, reusing established state where safe, and avoiding unnecessary coordination without weakening the correctness rules.
A demanding workload raises switching activity and heat, temperature approaches a threshold, control logic reduces clocks or voltage, heat generation falls, and performance may rise again after cooling creates enough margin. Each stage should validate what it receives before committing to the next stage. Timeouts and bounded retries handle ordinary loss, while explicit errors stop a bad state from silently spreading. Versions can differ, but a reliable implementation preserves the central contract and fails in a defined way when required evidence is absent or inconsistent. Recovery is part of the sequence too: after a restart or interrupted message, participants must know what was durable, what may repeat, and which operation can safely resume.
Throttling prevents immediate overheating, protects reliability, and allows devices to deliver short bursts of high performance within their cooling design. The improvement is strongest when surrounding components respect the same assumptions. Monitoring still matters because averages can hide one failed region, unusual client, or slow path. Engineers compare success rates, latency, capacity, and error causes before deciding that a deployment is working as intended. A sound design therefore connects the technical advantage to a measurable service goal rather than assuming that the mere presence of the feature creates value.
It cannot fix blocked airflow, failed fans, dried thermal material, unsafe overclocking, or a workload that continuously exceeds cooling capacity. Repeated throttling causes inconsistent performance. Compatibility and safe defaults also matter during upgrades because old and new behavior may coexist. A mixed environment creates fallback and configuration risk if teams cannot see which path a request used. Defense in depth treats this mechanism as one layer rather than the entire system. Human decisions remain important: broad permissions, unreviewed defaults, missing alarms, or a recovery procedure that nobody has tested can defeat an otherwise careful technical design.
Users clean vents, maintain fans and thermal interfaces, update firmware, avoid obstructing mobile devices, monitor sustained temperatures and clocks, and choose cooling sized for the intended power level. Documentation should record ownership, expected behavior, failure modes, and a tested recovery route. Changes are safest when introduced gradually with metrics and a way to reverse them. The operational question is not simply whether a feature is enabled, but whether surrounding identities, policies, capacity, versions, and human procedures make its promise true. Teams should rehearse the most likely failure, confirm that alerts reach an accountable person, and review settings after major workload, software, or threat changes.
No. It is a normal protection mechanism, though frequent throttling can reveal inadequate cooling or unrealistic power settings.
The chip may begin at a short boost level and then settle when temperature or sustained power reaches its limit.
It can preserve higher clocks when heat is the limiting factor, but voltage, current, firmware, and workload limits still apply.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.