

Smart Card Authentication Explainer
A smart card is a credential with an integrated circuit that can store protected data and perform cryptographic operations. Unlike a printed card or a magnetic stripe, it does not merely present a static identifier for another system to compare. A properly designed smart card can prove that it holds a private key without sending that key to the reader. This makes the card useful for building access, government credentials, employee logins, payments, and other systems that need stronger evidence than a typed password alone.
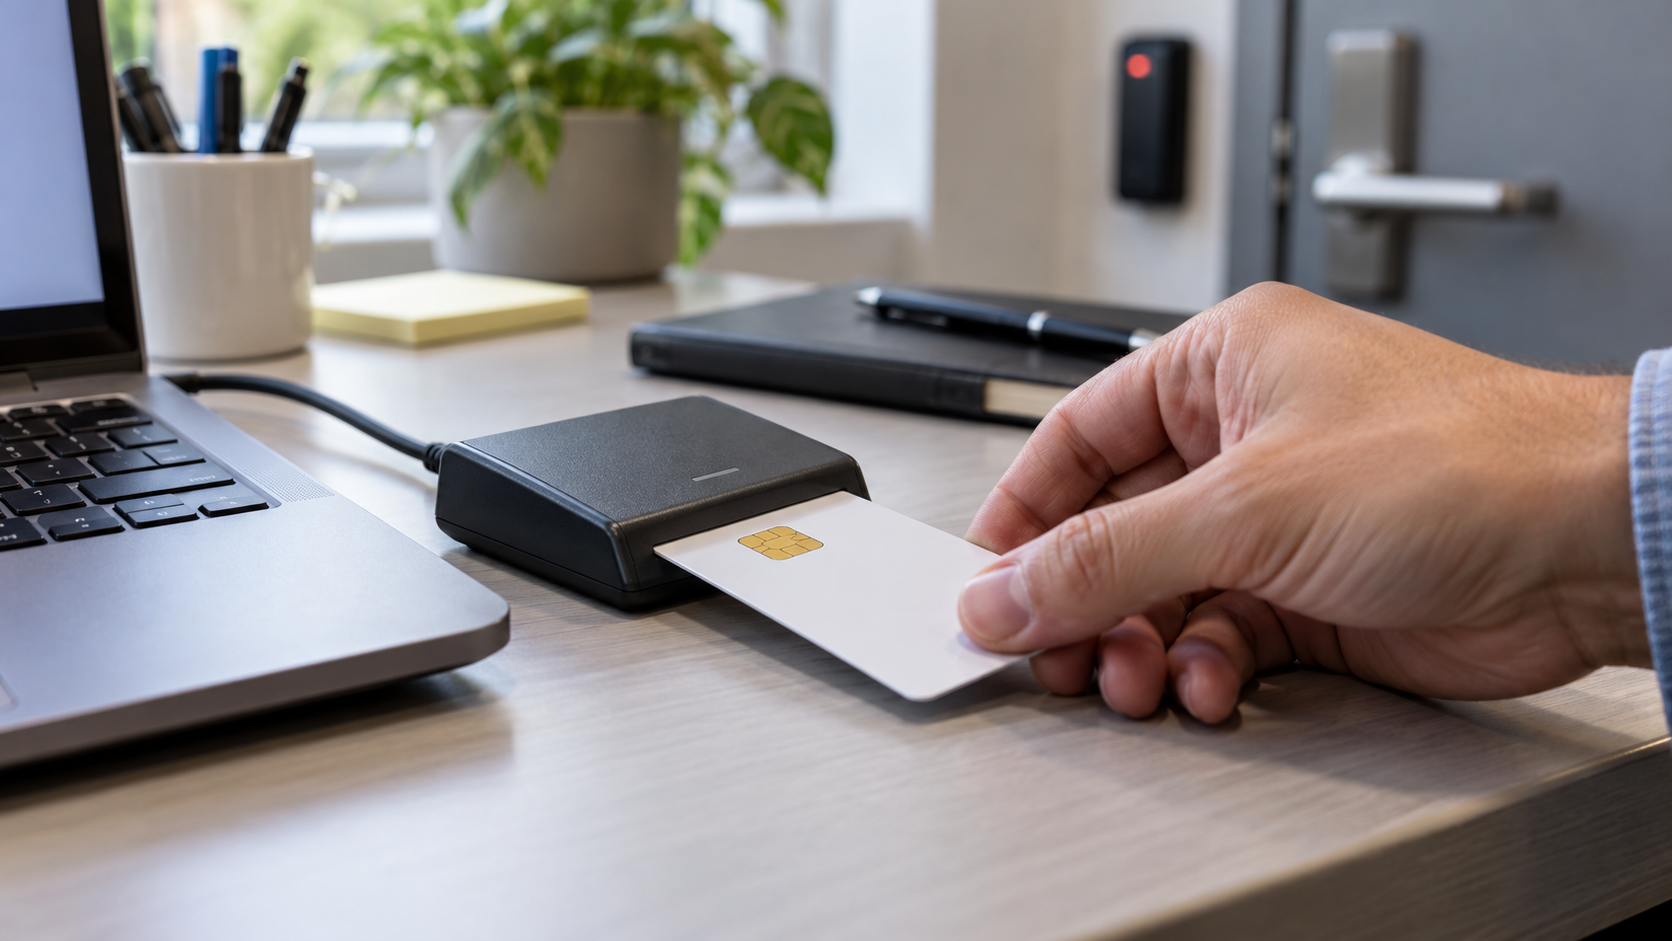
Authentication begins when a contact card is inserted into a reader or a contactless card is brought within radio range. The reader supplies power and exchanges structured commands with an application on the chip. The host selects the required card application, reads permitted identifiers or certificates, and may ask the user to activate protected functions with a personal identification number. The reader is the bridge, but the card’s chip enforces rules about which data can be read and which operations require successful PIN verification.
For a cryptographic challenge, the relying system creates a fresh, unpredictable value and sends it to the card. The chip signs or otherwise processes that challenge with a private key held inside protected storage. The system verifies the response with the corresponding public key, often using a certificate chain that links the credential to an issuing authority. Because each challenge is new, copying an earlier response should not be enough to log in later. The result can be combined with the cardholder’s identity and authorization records before access is granted.
The card and PIN represent different factors: something the user possesses and something the user knows. Some deployments add a biometric comparison or choose among several authentication mechanisms according to the sensitivity of the action. Federal Personal Identity Verification systems, for example, define card applications, certificates, PIN-controlled key use, and graduated authentication methods rather than treating every card interaction as equally strong. A simple visual inspection of a card is not the same as cryptographic authentication, and a contactless identifier by itself may provide only limited assurance.
Smart cards reduce some risks, but they do not make the surrounding system trustworthy by themselves. A stolen card can still be abused if a PIN is weak or captured, and a compromised reader or computer may mislead the user or alter an access request. Certificates expire and may need revocation after loss, employment changes, or a suspected key compromise. Implementations must limit failed PIN attempts, protect card-management channels, validate certificate status, secure readers, and consider relay, side-channel, and supply-chain attacks. Recovery procedures also matter because locked, damaged, or forgotten cards can prevent legitimate work.
The central security benefit is that a reusable secret can remain inside a dedicated chip. The user presents the physical credential, activates it when required, and lets the card perform a narrow proof instead of exposing the private key to an ordinary application. Effective deployments pair that property with trusted enrollment, careful issuance, lifecycle management, audit logs, and a clear link between authentication and authorization. They also provide a controlled replacement path and train users to notice unexpected PIN prompts. A smart card therefore works best as one component in a complete identity system, not as a stand-alone guarantee that every reader, network, and backend is safe. Administrators should test both normal and exceptional paths: offline verification, a revoked credential, a locked PIN, an unavailable certificate service, and emergency access. Privacy design is important too, because a stable card identifier can enable tracking if it is exposed more widely than necessary. The strongest program minimizes disclosed data, separates authentication records from unrelated monitoring, and documents who can issue, suspend, replace, and audit each credential.
The chip can protect private keys, PIN retry counters, and credential data under rules set by its operating system and card application. A private key can be used for a proof without being exported.
Public certificates and identifiers may be readable because they are meant for verification. Their availability does not reveal the corresponding private key.
The verifier sends a fresh challenge, and the card performs a cryptographic operation with its protected key. The verifier checks the result with a public key and rejects stale or invalid responses.
Certificates can connect that public key to an issuer and identity. Authorization is a separate decision made after the authentication evidence is accepted.
Cards can be lost, stolen, damaged, relayed, or used through a compromised reader. Weak PIN handling, poor certificate validation, and slow revocation can undermine the protected chip.
Operators need secure enrollment, reader management, retry limits, revocation, replacement procedures, and monitoring. Higher-risk uses may require additional factors or supervised processes.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.