

What Is a Hardware Security Module? Explainer
A hardware security module, or HSM, is a physical computing device designed to safeguard cryptographic keys and perform cryptographic operations. Instead of storing a private key as an ordinary file that application software can read, an HSM keeps the key inside a defined security boundary. An authorized application sends a request such as “sign this digest,” “decrypt this wrapped key,” or “generate a new key.” The module performs the operation and returns the result without normally revealing the protected private key to the application.
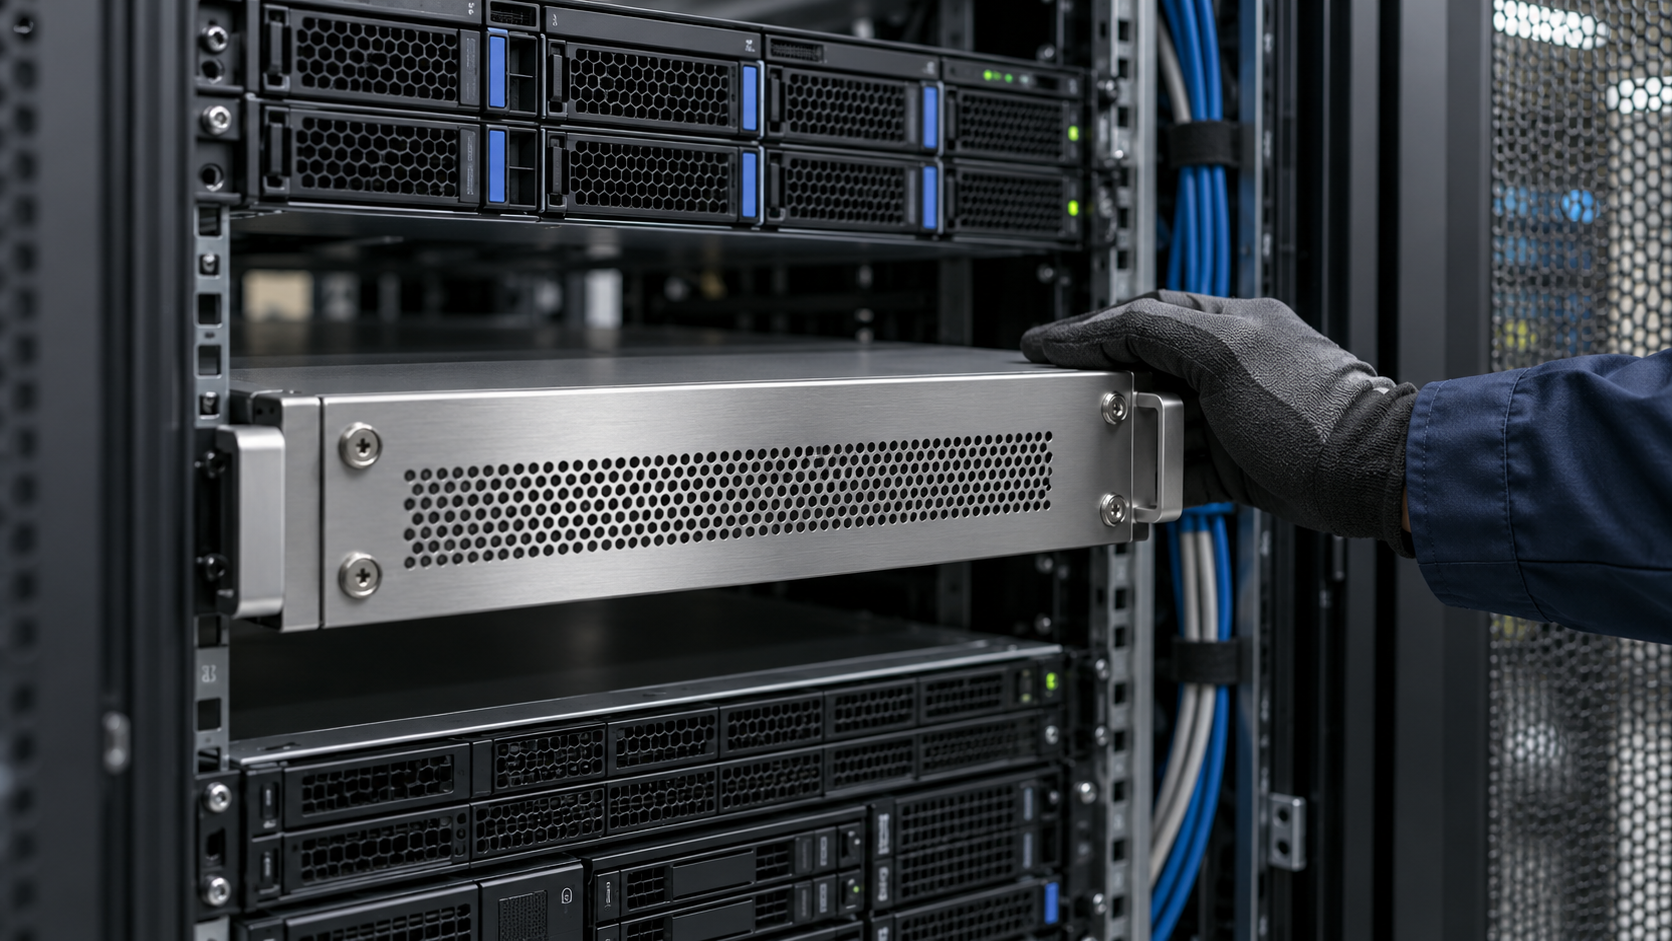
HSMs appear in several forms. A data center may use a network-attached appliance shared by multiple services, an expansion card inside a server, or an embedded module built into another product. The device contains cryptographic processing, protected memory, firmware, authentication controls, and interfaces for key creation, backup, import, export, or deletion according to policy. Some models use tamper-evident or tamper-responsive enclosures and erase sensitive material when physical intrusion is detected. High availability deployments may cluster modules, but every replica and backup becomes part of the key-management system that must be secured.
Access is usually separated by roles and permissions. Administrators configure the device and its partitions, security officers establish policy, and applications authenticate before using particular key objects. Keys can be marked non-exportable, restricted to approved algorithms, or limited to signing, encryption, or key-wrapping operations. Audit records can show which identity requested an operation and when. Because the module performs the cryptography, it can also provide a controlled source of randomness and enforce policies that ordinary application code might accidentally bypass.
Standards and validation help buyers evaluate a cryptographic module, but labels require careful reading. FIPS 140-3 defines security requirement areas that include interfaces, roles, authentication, physical security, sensitive-parameter management, self-tests, and life-cycle assurance. Validation applies to a specific module version, configuration, and operating environment listed in its certificate and security policy. It does not guarantee that every surrounding application is secure, that administrators will manage keys correctly, or that the device resists every imaginable attack.
Common uses reflect the value of keeping a root secret in one controlled place. A certificate authority can sign certificates, a payment system can protect transaction keys, a company can hold code-signing keys, and a cloud service can give customers isolated key partitions. Many designs use a hierarchy: a long-lived master key inside the HSM wraps other keys that may be stored outside only in encrypted form. When an application needs one of those keys, the module unwraps it internally for an authorized operation. This reduces exposure but also concentrates trust, so key generation, migration, destruction, and recovery ceremonies must be documented and tested before an outage or compromise forces urgent action. Performance planning matters because public-key signing, bulk encryption, and random-number generation use different resources. Organizations often keep high-volume data encryption in ordinary systems while using the HSM to protect the smaller key-encryption keys that control access to that data. That division preserves a hardware root of trust without forcing every byte through the module.
An HSM also creates operational responsibilities. Organizations need secure provisioning, quorum or dual-control procedures for critical changes, monitored backups, disaster recovery, capacity planning, firmware governance, and a method to rotate or revoke keys. Network latency and transaction limits may affect high-volume services. A compromised application might still ask an authorized HSM to perform harmful operations even if it cannot extract the key, so request authorization and application security remain essential. The value of an HSM is concentrated control: it reduces the number of places secret keys exist in readable form and moves important cryptographic operations into hardware designed to enforce explicit boundaries. Governance remains essential.
An HSM is a physical device that protects cryptographic keys and performs operations without normally exposing private key material. Key terms include cryptographic module, security boundary, non-exportable key, signing, key wrapping, partition, role, audit log, tamper response, dual control, and FIPS 140-3.
An authenticated application sends data and an operation request to the module. The HSM checks permissions, uses the selected protected key internally, and returns a signature, ciphertext, plaintext, or wrapped object. Export rules determine whether any key material can leave the boundary.
Validation shows that a specific module version and configuration was tested against defined requirements. It does not certify every product using the module or replace secure application design, access control, key ceremonies, backups, monitoring, and correct operation.
Explore more "Explainers"
Discover additional explainers across politics, science, business, technology, and other fields. Each explainer breaks down a complex idea into clear, everyday language—helping you better understand how major concepts, systems, and debates shape the world around us.